New AI-Infused Malware Targets Victims with Unprecedented Data Theft
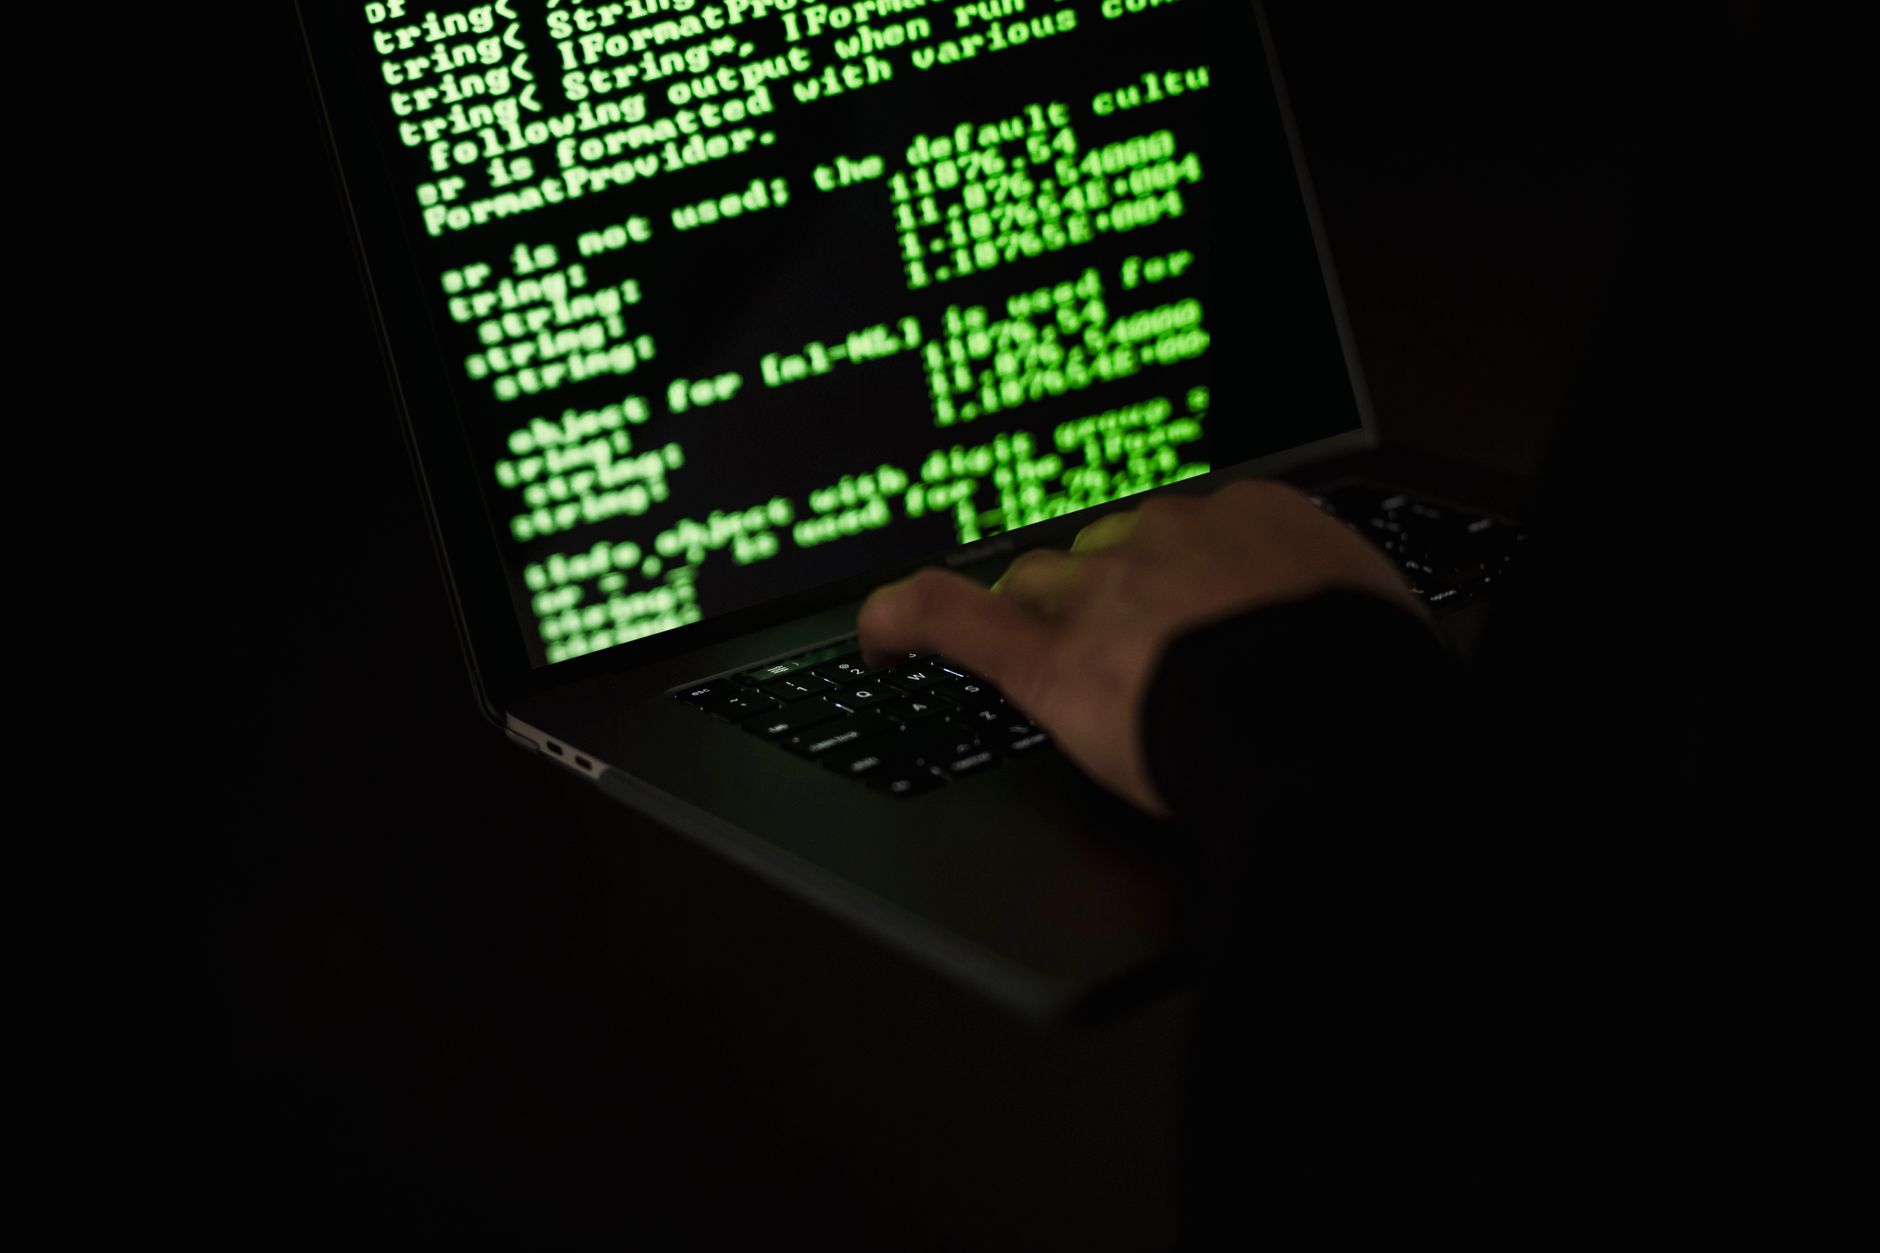
A recently identified malware, dubbed “Volta-Autodoxer,” is raising alarm bells in the cybersecurity community as it employs artificial intelligence to launch a sophisticated assault on personal data. This innovative malware is capable of harvesting a wide range of sensitive information from its victims, including login credentials, credit card details, and even interactions on platforms like Discord and UberEats.
What sets Volta-Autodoxer apart from traditional infostealers is its use of AI technologies to enhance its data-gathering capabilities. This allows the malware to operate more efficiently and adaptively, making it a formidable threat in the ever-evolving landscape of cybercrime. Cybersecurity experts are particularly concerned about the ease with which Volta-Autodoxer can infiltrate devices and the depth of data it can extract.
Upon infection, the malware begins a relentless process of data collection, targeting not only financial information but also personal communications and other digital footprints left by users. The AI component enables it to analyze and prioritize which data to steal, ensuring that attackers obtain the most valuable information first. This intelligence-driven approach allows cybercriminals to exploit their targets more effectively, increasing the potential for identity theft and financial fraud.
Researchers first detected Volta-Autodoxer in late September, and its rapid proliferation has sparked a wave of warnings from cybersecurity firms. The malware can be distributed through various channels, including phishing emails and malicious downloads, making it crucial for users to remain vigilant about their online behavior. Those who are unaware of the threat may unwittingly install the malware, opening the door to rampant data theft.
In response to this emerging threat, cybersecurity experts are urging individuals to take proactive measures to protect their personal information. Implementing strong, unique passwords for different accounts and enabling two-factor authentication can significantly reduce the risk of falling victim to attacks like those orchestrated by Volta-Autodoxer. Additionally, regular updates to software and operating systems can help close vulnerabilities that malware might exploit.
As the digital landscape continues to become more complex and interconnected, threats like Volta-Autodoxer highlight the importance of cybersecurity awareness and the need for ongoing advancements in protective technologies. The stakes are high, and as more sophisticated tools become available to cybercriminals, individuals and organizations must remain on guard to protect their valuable data from being compromised.